STALLED CODEBASE? GHOSTED BY DEVS?
I TAKE COMMAND AND SHIP IN 30 DAYS.
Stop losing sleep over broken code. Work directly with Blaise Pascual—former Marine officer, builder of Mirror (iOS & Android), and founder of nootropic.ai. I audit your codebase for free in 72 hours, then stabilize and ship your app in 30 days for $5,000 flat.
I Don't Just Build Apps for Clients. I Build, Launch, and Monetize My Own.
I'm Blaise Pascual—veteran, former USMC officer, and senior full-stack software engineer. Most agencies hand your app to junior developers or offshore brokers. When you hire me, I write, test, and ship your software directly.
For web, I founded and actively build nootropic.ai—a live AI web platform for cognitive performance and stack optimization (mobile release pending). For mobile, I built and shipped Mirror (mirrorapp.ai) for a client to both the App Store and Google Play.
"The same architecture, security, and release discipline behind my live products goes into yours."
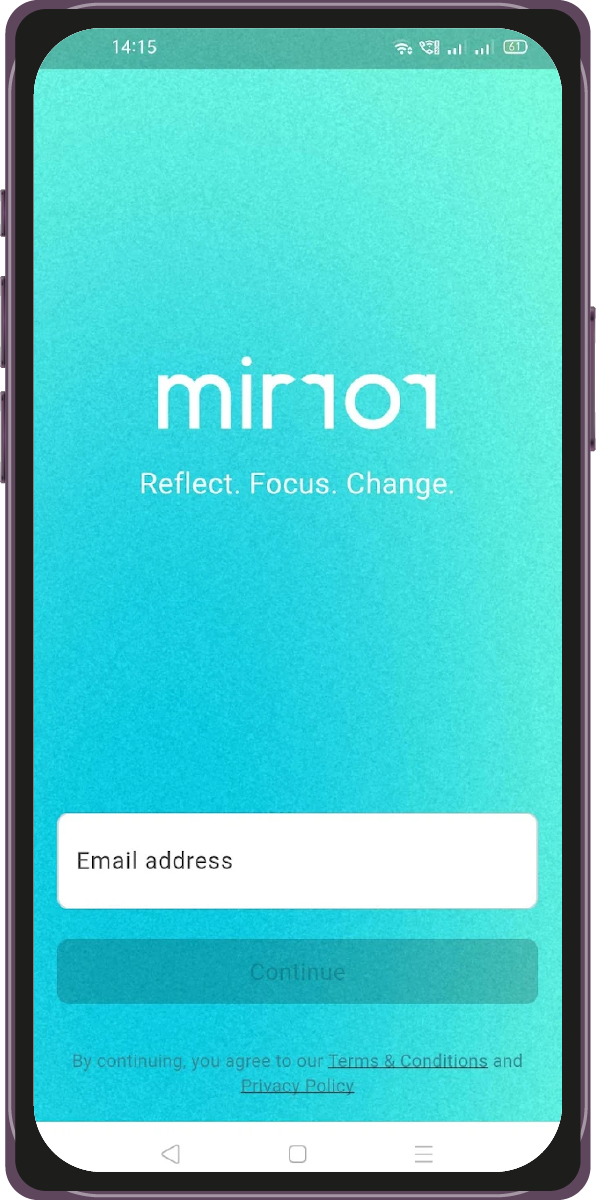
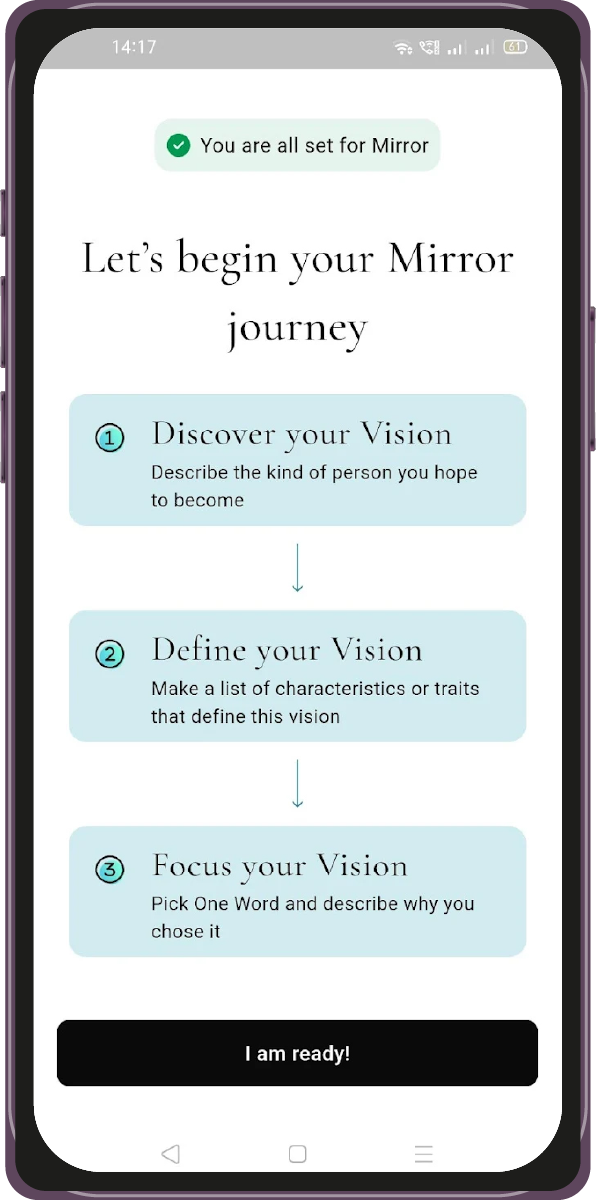
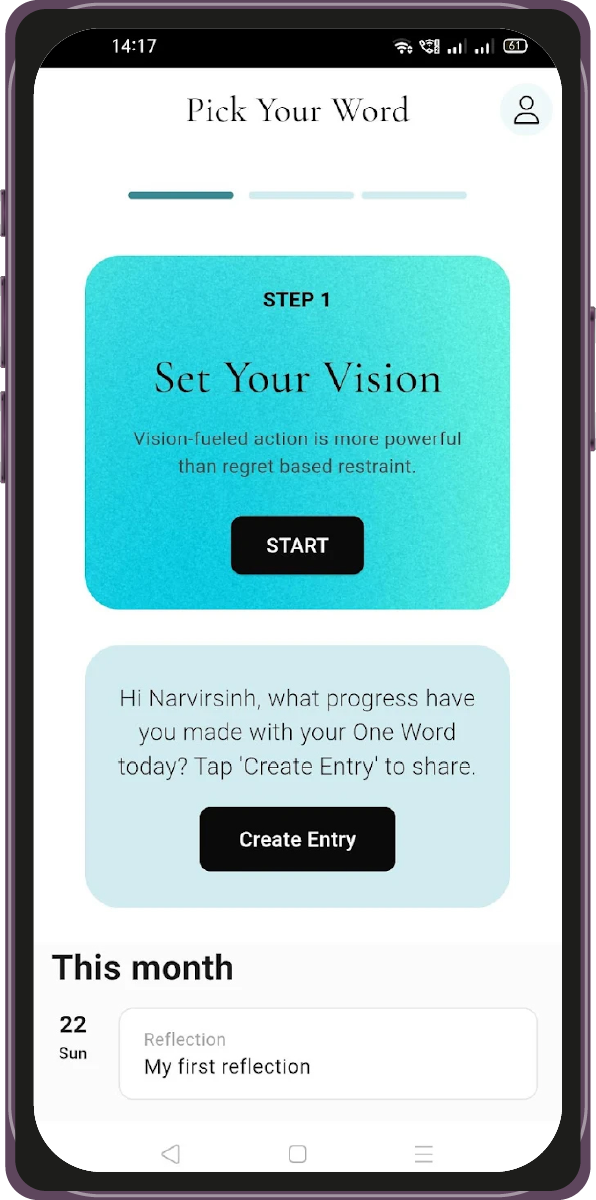
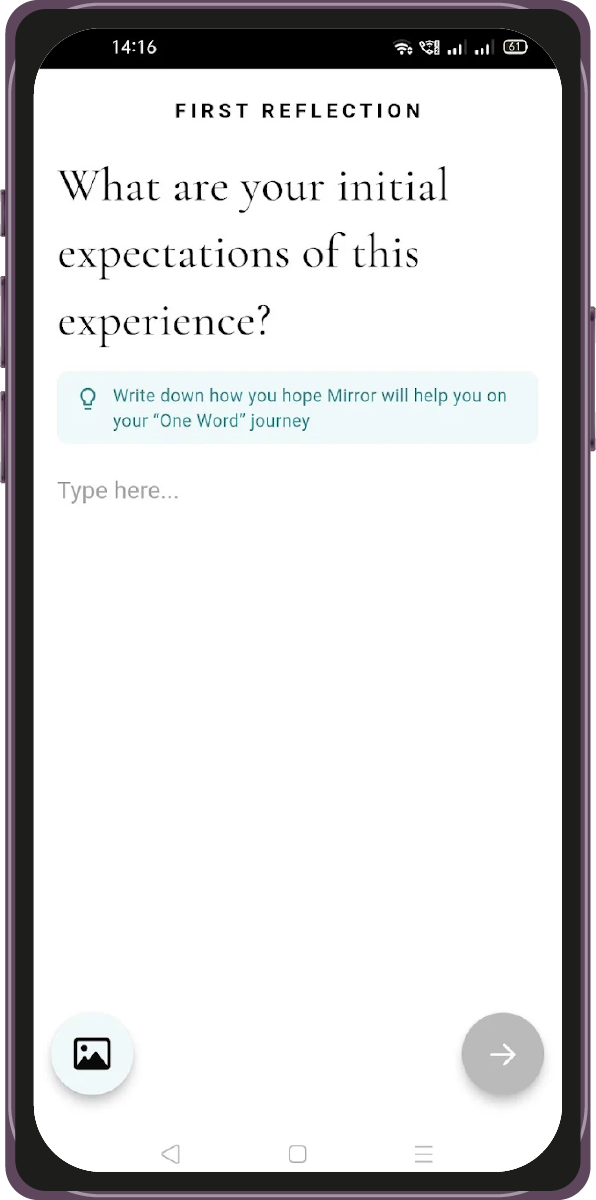
Mirror is published on both iOS and Android after clearing real store review—not a prototype.
Zero API keys or database credentials sit on user devices. Every request runs through signed server proxies.
Code signing, metadata, privacy disclosures, and store compliance handled end-to-end.
You own every line of code, database, and store account from Day 1. Zero lock-in.
Mirror: Shipped to the App Store & Google Play
Web App Case Study: nootropic.ai
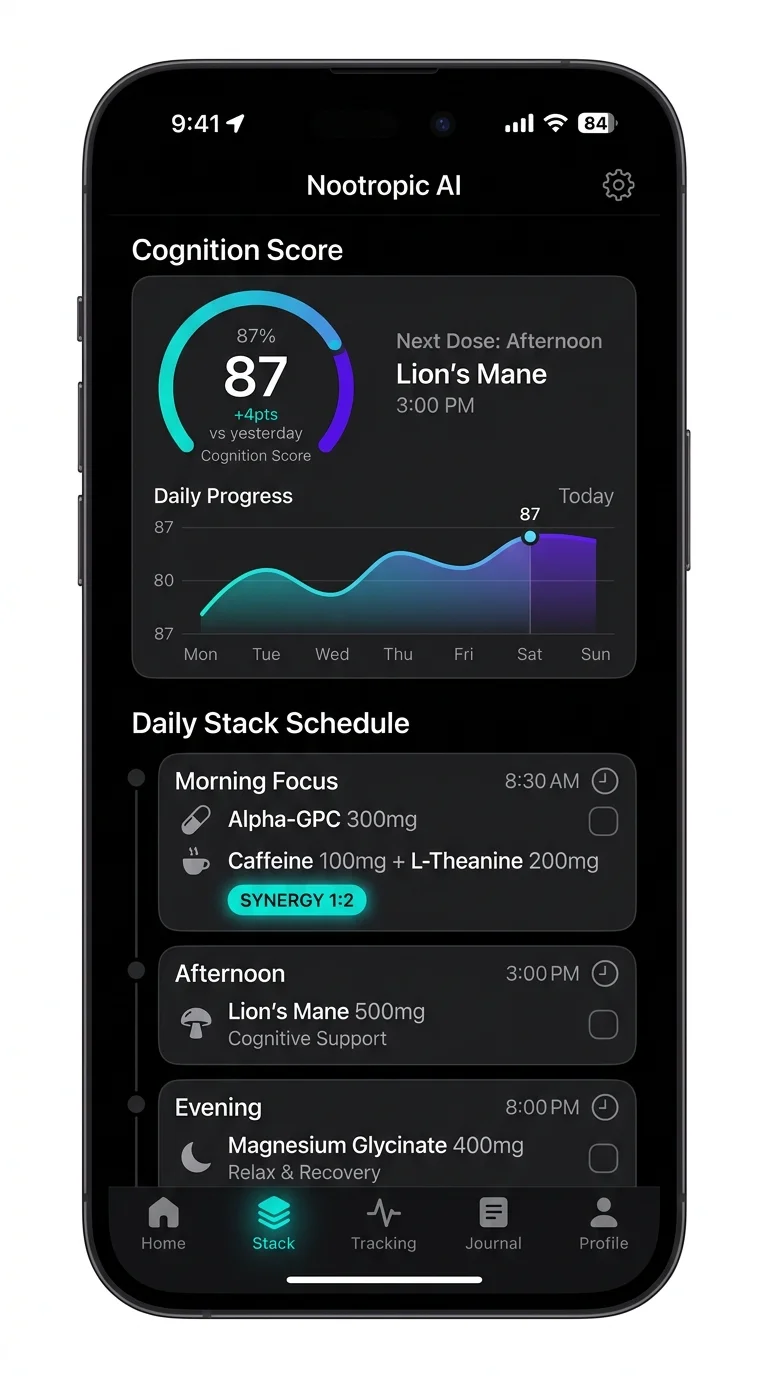
Daily supplement scheduling, 1:2 synergy ratios, and cognition score tracking.
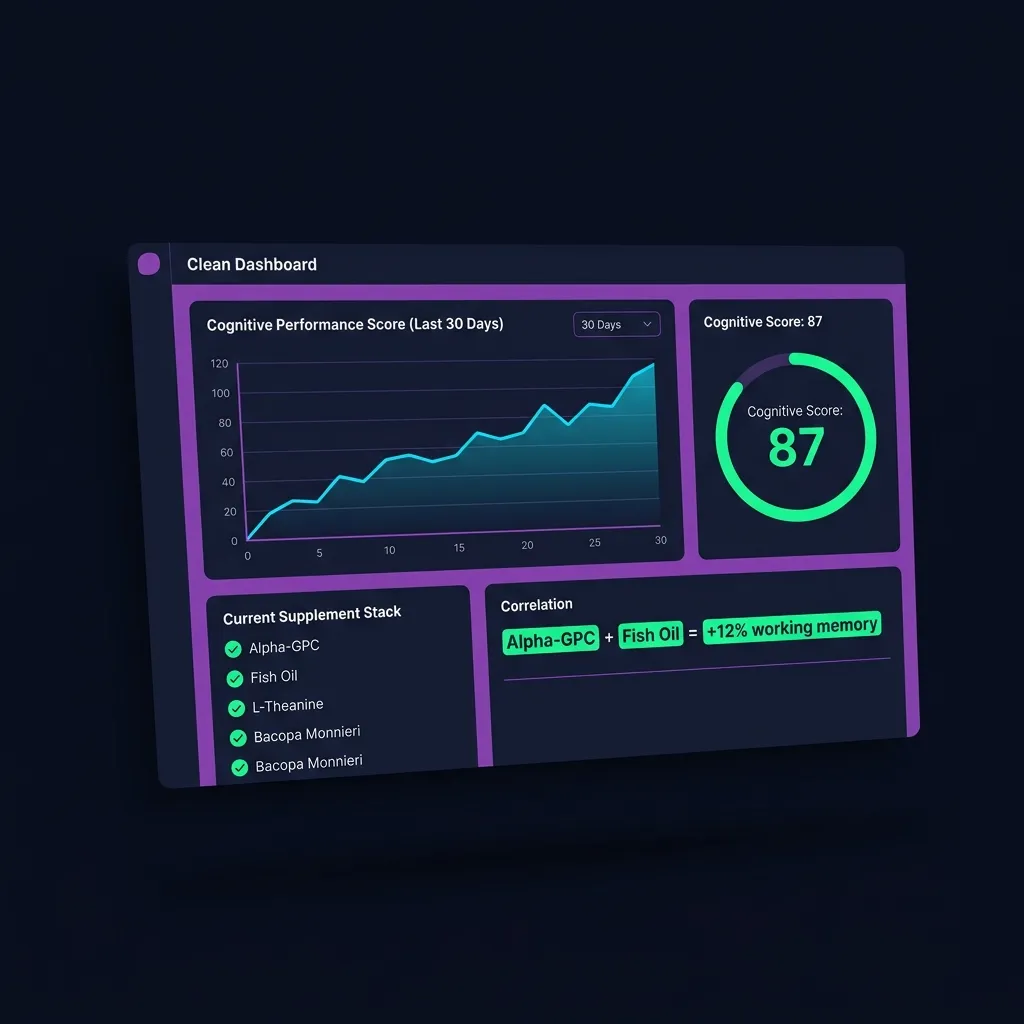
Cognitive score 87, 30-day baseline trend, and nutrient correlation engine.
Evidence-backed pharmacology with automated contraindication detection.
Digital tracking for compound expiration, half-life degradation, and restocks.
Interactive Forensic Vulnerability Inspector
Compare real code diffs from stalled offshore builds against Paladin’s hardened architectural refactors. Inspect real CVEs, blast radii, and surgical remediation patches.
// ❌ OFFSHORE CLIENT CODE (App.tsx / config.ts)
// CRITICAL: Bundling full admin service_role secret into public iOS/Android binary
import { createClient } from '@supabase/supabase-js';

const SUPABASE_URL = "https://xyzcompany.supabase.co";
// Leaked admin key bypasses all Row-Level Security!
const SUPABASE_SERVICE_KEY = "eyJhbGciOiJIUzI1NiIsInR5cCI6IkpXVCJ9.eyJy...SECRET_ROLE_KEY";
const OPENAI_SECRET = "sk-proj-94820491823901238910283910283";

export const supabase = createClient(SUPABASE_URL, SUPABASE_SERVICE_KEY);

export async function askAI(prompt: string) {
  // Direct client-side billing vulnerability: anyone decompiling APK drains your OpenAI bill
  return fetch("https://api.openai.com/v1/chat/completions", {
    headers: { Authorization: `Bearer ${OPENAI_SECRET}` },
    body: JSON.stringify({ model: "gpt-4o", messages: [{ role: "user", content: prompt }] })
  });
}Offshore developers hardcoded admin service_role credentials and OpenAI keys directly into the client bundle. Anyone decompiling the app can dump your database and drain your API billing.
// ✅ PALADIN HARDENED ARCHITECTURE (supabase/functions/llm-proxy/index.ts)
// Sovereign Edge Gateway: Zero secrets in client. Session verified via signed JWT.
import { serve } from "https://deno.land/std@0.168.0/http/server.ts";
import { createClient } from "https://esm.sh/@supabase/supabase-js@2";

serve(async (req: Request) => {
  const authHeader = req.headers.get("Authorization");
  if (!authHeader) return new Response("Unauthorized", { status: 401 });

  // 1. Verify authenticated user identity server-side
  const supabase = createClient(
    Deno.env.get("SUPABASE_URL")!,
    Deno.env.get("SUPABASE_ANON_KEY")!,
    { global: { headers: { Authorization: authHeader } } }
  );
  const { data: { user }, error } = await supabase.auth.getUser();
  if (error || !user) return new Response("Forbidden", { status: 403 });

  // 2. Enforce atomic server-side rate limits & token bucket
  // 3. Isolated secret resolution from encrypted environment store
  const apiKey = Deno.env.get("OPENAI_API_KEY")!;
  const payload = await req.json();

  const aiRes = await fetch("https://api.openai.com/v1/chat/completions", {
    method: "POST",
    headers: { "Content-Type": "application/json", Authorization: `Bearer ${apiKey}` },
    body: JSON.stringify({ model: "gpt-4o", messages: payload.messages, user: user.id }),
  });

  return new Response(aiRes.body, { headers: { "Content-Type": "application/json" } });
});Revoke leaked credentials, scrub Git history with BFG, and route all sensitive calls through a signed Supabase Edge Function proxy.
The 25-Point Comprehensive Forensic Scope
Every rescue begins with my rigorous 25-point sweep across credentials, schemas, state, and store policies.
1. Sovereign Credential & Key Hygiene
- Purge hardcoded OpenAI, Anthropic, Stripe, and Supabase service keys from source
- BFG Repo-Cleaner scrub to eradicate leaked secrets from historical Git commits
- Immediate revocation and regeneration of all third-party API tokens & OAuth client secrets
- Implementation of `.env.local` encryption and separation from CI/CD production pipelines
- Migration of all administrative calls to isolated, authenticated Edge Microservices
2. Database RLS & API Authorization
- Execution of comprehensive `ENABLE ROW LEVEL SECURITY` across 100% of public tables
- Strict tenant isolation policies enforcing `auth.uid() = user_id` on SELECT/UPDATE/DELETE
- Revocation of dangerous public and anonymous table privileges on PostgreSQL schemas
- Database index audit on foreign keys to eliminate 5-second unindexed table scan queries
- Hardening of custom RPC database functions with explicit `SECURITY DEFINER` sandboxing
3. Mobile State & Concurrency
- Elimination of unbounded loop conditions causing CPU throttling & battery drain
- Replacement of unvirtualized layouts with hardware-accelerated recyclable lists
- Memory leak elimination: clean teardown of native WebSocket and event subscriptions
- Implementation of atomic client cache invalidation and background hydration
- Hardware asset optimization: migrating to GPU-rendered native image caching
4. Apple Store Review Compliance Armor
- Apple Guideline 5.1.1 compliance: Transactional account and cloud cascade deletion flow
- Apple Guideline 3.1.1 compliance: RevenueCat StoreKit 2 native paywall and receipt validation
- Apple Guideline 4.2 compliance: Removal of generic web wrappers in favor of native UI components
- Hardware permission transparency: descriptive iOS Info.plist camera and push justifications
- Sign in with Apple integration when third-party OAuth (Google, Facebook) is present
5. Native CI/CD & Build Provenance
- Resolution of broken CocoaPods, Gradle, and mismatched native dependency versions
- Stabilization of automated, reproducible dual-platform cloud build pipelines
- Apple Developer provisioning profile, certificate, and bundle ID cleanup
- Automated Sentry error logging and PostHog user event telemetry wiring
- Successful TestFlight artifact generation delivered directly to the founder's inbox
Actionable Forensic Dossier
I don't give you high-level fluff. You receive an exhaustive line-by-line audit detailing exactly what code is salvageable, what must be purged, and the exact roadmap to a stable build.
The 72-Hour Rapid Quarantine Protocol
A systematic military-style lockdown that secures your intellectual property and outlines the surgical path to release.
Quarantine & Asset Recovery
Contain the breach, freeze the repository, and revoke compromised access.
- Complete inventory of third-party assets (GitHub, AWS, Supabase, Apple Dev, Stripe)
- Immediate revocation of offshore developer maintainer keys and SSH deploy credentials
- Git commit tree forensic scan; execution of BFG Repo-Cleaner to eliminate leaked tokens
- Installation of repository branch protection rules, signing keys, and audit logging
Architectural Decoupling & RLS Lockdown
Repair fatal database leaks, stabilize state machines, and shield APIs.
- Implementation of PostgreSQL Row-Level Security policies to seal cross-user data leakage
- Deployment of Supabase Edge Function proxy layers to isolate all LLM & payment secret keys
- Surgical remediation of circular dependency graphs, infinite re-render loops, and OOM crashes
- Refactoring of broken mobile authentication loops (Apple Sign In, Magic Links, PKCE flow)
Clean Build & Forensic Release Dossier
Compile clean native binaries, pass Store pre-flight, and hand over control.
- Native dual-platform compilation test with certified provisioning profiles and App Store icons
- Resolution of Apple rejection blockers (Account deletion flow, StoreKit paywall compliance)
- Generation of physical iOS / Android TestFlight internal build invitation
- Delivery of the executive Forensic Codebase Audit Dossier (What to keep, what was fixed, scale roadmap)
Complete Clarity in 72 Hours. Free.
Within 72 hours of repository handover, I deliver a blunt, line-by-line Forensic Security & Architecture Audit Dossier at no cost—yours to keep whether you hire me for the sprint or not. If you want me to fix it, the full 30-day rescue is $5,000 flat, with scope locked in writing before I write a single line.
Stop Bleeding Capital. Take Back Control Today.
Book a 1-on-1 codebase rescue call directly with Blaise Pascual. Share your current repository or project status under mutual NDA. I begin forensic inspection within 24 hours.